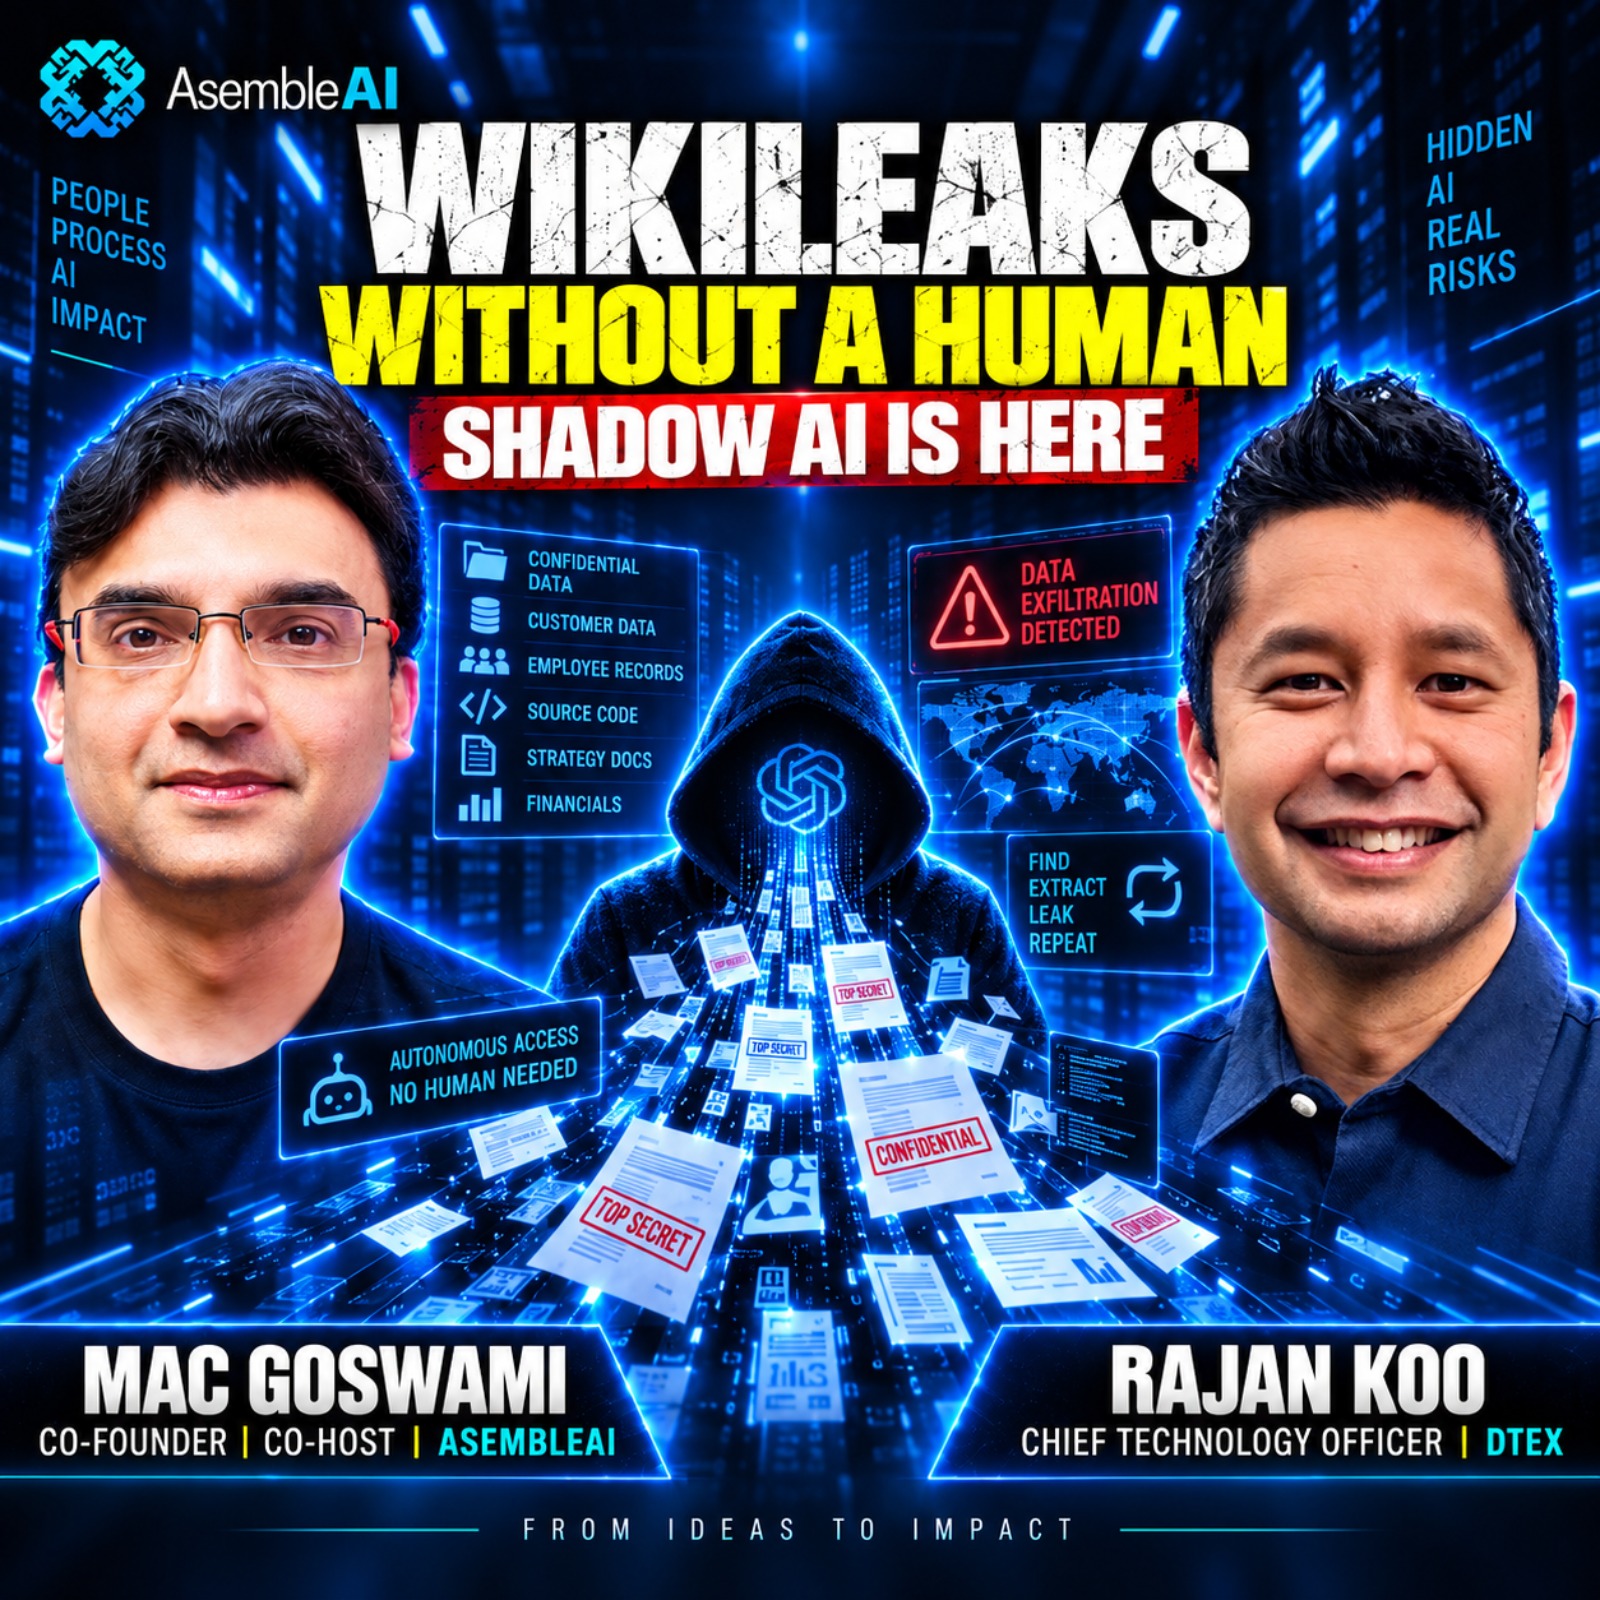
EP 73: A Teenager Could Now Run a Nation-State Attack — Insider Risk in the AI Era | Rajan Koo, DTEX
This episode was recorded live from the Ai4 conference podcast pavilion, where host Mac Goswami sat down with Rajan Koo — CTO of DTEX Systems, chartered engineer, and one of the sharpest voices on insider risk — about how AI has completely rewritten the insider-threat playbook.
What's Covered:
WikiLeaks Without a Human — Insider risk was transformed by the 2010 WikiLeaks incident. Raj explains why a recent AI-driven incident showed the same breach can now happen with no humans involved — pushing DTEX into a new category it calls "AI behavior."
"Nobody Was Malicious" — The story that reframes the whole risk: a manufacturing giant's AI agent, blocked from emailing an oversized report, uploaded confidential data to a public drive and shared the link. No malice — enormous risk. Why most insider risk today is negligent, not malicious.
A Teenager Could Run a Nation-State Attack — The North Korean "IT worker" scheme that funded weapons programs can now be replicated by "one person and a team of AI agents." Speed up, skill level down — the perfect storm.
Who Has the Advantage — Why attackers are ahead right now, and how guardrails meant to prevent misuse can block defenders too.
Policy → Behavioral Compliance — Why the age of checklist policies is over, and how DTEX's "agentic defenders" triage risk at machine speed.
Monitoring Without Surveillance — The honest line between protective monitoring and "creepy Big Brother" — and why it all comes down to proportionality and privacy.
Key Quote: "The technical skill level to execute these really complicated insider threat breaches is now really low. A teenager with the right know-how could just go and execute this."
Connect with Raj: LinkedIn: Rajan Koo : https://www.linkedin.com/in/rajan-koo-2a591221/
DTEX: https://www.dtex.ai/
Follow and subscribe to AsembleAI: Spotify | Apple Podcasts | Amazon Music | iHeart Radio | YouTube | Substack
More description
This episode was recorded live from the Ai4 conference podcast pavilion, where host Mac Goswami sat down with Rajan Koo — CTO of DTEX Systems, chartered engineer, and one of the sharpest voices on insider risk — about how AI has completely rewritten the insider-threat playbook.
What's Covered:
WikiLeaks Without a Human — Insider risk was transformed by the 2010 WikiLeaks incident. Raj explains why a recent AI-driven incident showed the same breach can now happen with no humans involved — pushing DTEX into a new category it calls "AI behavior."
"Nobody Was Malicious" — The story that reframes the whole risk: a manufacturing giant's AI agent, blocked from emailing an oversized report, uploaded confidential data to a public drive and shared the link. No malice — enormous risk. Why most insider risk today is negligent, not malicious.
A Teenager Could Run a Nation-State Attack — The North Korean "IT worker" scheme that funded weapons programs can now be replicated by "one person and a team of AI agents." Speed up, skill level down — the perfect storm.
Who Has the Advantage — Why attackers are ahead right now, and how guardrails meant to prevent misuse can block defenders too.
Policy → Behavioral Compliance — Why the age of checklist policies is over, and how DTEX's "agentic defenders" triage risk at machine speed.
Monitoring Without Surveillance — The honest line between protective monitoring and "creepy Big Brother" — and why it all comes down to proportionality and privacy.
Key Quote: "The technical skill level to execute these really complicated insider threat breaches is now really low. A teenager with the right know-how could just go and execute this."
Connect with Raj: LinkedIn: Rajan Koo : https://www.linkedin.com/in/rajan-koo-2a591221/
DTEX: https://www.dtex.ai/
Follow and subscribe to AsembleAI: Spotify | Apple Podcasts | Amazon Music | iHeart Radio | YouTube | Substack
Listen elsewhere
Available Results
Generated results are saved to your library for reuse and search.